Case Study
This is a case study. Case studies are not timed separately. You can use as much exam time as you would like to complete each case. However, there may be additional case studies and sections on this exam. You must manage your time to ensure that you are able to complete all questions included on this exam in the time provided.
To answer the questions included in a case study, you will need to reference information that is provided in the case study. Case studies might contain exhibits and other resources that provide more information about the scenario that is described in the case study. Each question is independent of the other questions in this case study.
At the end of this case study, a review screen will appear. This screen allows you to review your answers and to make changes before you move to the next section of the exam. After you begin a new section, you cannot return to this section.
To start the case study
To display the first question in this case study, click the Next button. Use the buttons in the left pane to explore the content of the case study before you answer the questions. Clicking these buttons displays information such as business requirements, existing environment, and problem statements. If the case study has an All Information tab, note that the information displayed is identical to the information displayed on the subsequent tabs.
When you are ready to answer a question, click the Question button to return to the question.
Overview
Litware, Inc. is an independent software vendor (ISV). Litware has a main office and five branch offices.
Existing Environment
Application Architecture
The company’s primary application is a single monolithic retirement fund management system based on ASP.NET web forms that use logic written in VB.NET. Some new sections of the application are written in C#.
Variations of the application are created for individual customers. Currently, there are more than 80 live code branches in the application’s code base.
The application was developed by using Microsoft Visual Studio. Source code is stored in Team Foundation Server (TFS) in the main office. The branch offices access the source code by using TFS proxy servers.
Architectural Issues
Litware focuses on writing new code for customers. No resources are provided to refactor or remove existing code. Changes to the code base take a long time, as dependencies are not obvious to individual developers.
Merge operations of the code often take months and involve many developers. Code merging frequently introduces bugs that are difficult to locate and resolve.
Customers report that ownership costs of the retirement fund management system increase continually. The need to merge unrelated code makes even minor code changes expensive.
Customers report that bug reporting is overly complex.
Requirements
Planned Changes
Litware plans to develop a new suite of applications for investment planning. The investment planning applications will require only minor integration with the existing retirement fund management system.
The investment planning applications suite will include one multi-tier web application and two iOS mobile applications. One mobile application will be used by employees; the other will be used by customers.
Litware plans to move to a more agile development methodology. Shared code will be extracted into a series of packages.
Litware has started an internal cloud transformation process and plans to use cloud-based services whenever suitable.
Litware wants to become proactive in detecting failures, rather than always waiting for customer bug reports.
Technical Requirements
The company’s investment planning applications suite must meet the following technical requirements:
-New incoming connections through the firewall must be minimized.
-Members of a group named Developers must be able to install packages.
-The principle of least privilege must be used for all permission assignments.
-A branching strategy that supports developing new functionality in isolation must be used.
-Members of a group named Team Leaders must be able to create new packages and edit the permissions of package feeds.
-Visual Studio App Center must be used to centralize the reporting of mobile application crashes and device types in use.
-By default, all releases must remain available for 30 days, except for production releases, which must be kept for 60 days.
-Code quality and release quality are critical. During release, deployments must not proceed between stages if any active bugs are logged against the release.
-The mobile applications must be able to call the share pricing service of the existing retirement fund management system. Until the system is upgraded, the service will only support basic authentication over HTTPS.
-The required operating system configuration for the test servers changes weekly. Azure Automation State Configuration must be used to ensure that the operating system on each test server is configured the same way when the servers are created and checked periodically.
Current Technical Issue
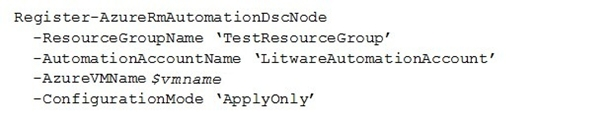
The test servers are configured correctly when first deployed, but they experience configuration drift over time. Azure Automation State Configuration fails to correct the configurations.
Azure Automation State Configuration nodes are registered by using the following command.