Case study:
This is a case study. Case studies are not timed separately. You can use as much exam time as you would like to complete each case. However, there may be additional case studies and sections on this exam. You must manage your time to ensure that you are able to complete all questions included on this exam in the time provided.
To answer the questions included in a case study, you will need to reference information that is provided in the case study. Case studies might contain exhibits and other resources that provide more information about the scenario that is described in the case study. Each question is independent of the other questions in this case study.
At the end of this case study, a review screen will appear. This screen allows you to review your answers and to make changes before you move to the next section of the exam. After you begin a new section, you cannot return to this section.
To start the case study To display the first question in this case study, click the Next button. Use the buttons in the left pane to explore the content of the case study before you answer the questions. Clicking these buttons displays information such as business requirements, existing environment, and problem statements. If the case study has an All Information tab, note that the information displayed is identical to the information displayed on the subsequent tabs.
When you are ready to answer a question, click the Question button to return to the question.
Overview
Litware Inc. is a renewable energy company.
Litware has offices in Boston and Seattle. Litware also has remote users located across the United States. To access Litware resources, including cloud resources, the remote users establish a VPN connection to either office.
Existing Environment
Identity Environment
The network contains an Active Directory forest named litware.com that syncs to a Microsoft Entra tenant named litware.com.
Microsoft 365 Environment
Litware has a Microsoft 365 E5 subscription linked to the litware.com Microsoft Entra tenant. Microsoft Defender for Endpoint is deployed to all computers that run Windows 10. All Microsoft Defender for Cloud Apps built-in anomaly detection policies are enabled.
Azure Environment
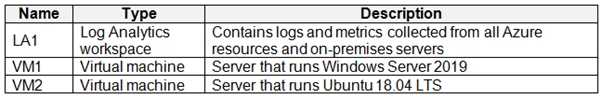
Litware has an Azure subscription linked to the litware.com Microsoft Entra tenant. The subscription contains resources in the East US Azure region as shown in the following table.
Network Environment
Each Litware office connects directly to the internet and has a site-to-site VPN connection to the virtual networks in the Azure subscription.
On-premises Environment
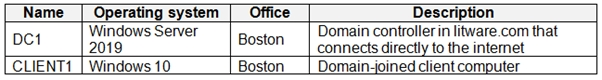
The on-premises network contains the computers shown in the following table.
Current problems
Microsoft Defender for Cloud Apps frequently generates false positive alerts when users connect to both offices simultaneously.
Planned Changes and Requirements
Planned Changes
Litware plans to implement the following changes:
-Create and configure Azure Sentinel in the Azure subscription.
-Validate Azure Sentinel functionality by using Microsoft Entra test user accounts.
Business Requirements
Litware identifies the following business requirements:
-The principle of least privilege must be used whenever possible.
-Costs must be minimized, as long as all other requirements are met.
-Logs collected by Log Analytics must provide a full audit trail of user activities.
-All domain controllers must be protected by using Microsoft Defender for Identity.
Azure Information Protection Requirements
All files that have sensitivity labels and are stored on the Windows 10 computers must be available from the Azure Information Protection – Data discovery dashboard.
Microsoft Defender for Endpoint Requirements
All Microsoft Defender for Cloud Apps unsanctioned apps must be blocked on the Windows 10 computers by using Microsoft Defender for Endpoint.
Microsoft Defender for Cloud Apps Security Requirements
Microsoft Defender for Cloud Apps must identify whether a user connection is anomalous based on tenant-
level data.
Microsoft Defender for Cloud Requirements
All servers must send logs to the same Log Analytics workspace.
Microsoft Sentinel Requirements
Litware must meet the following Microsoft Sentinel requirements:
-Integrate Microsoft Sentinel and Microsoft Defender for Cloud Apps.
-Ensure that a user named admin1 can modify existing Microsoft Sentinel playbooks.
-Create an Microsoft Sentinel analytics rule based on a custom query. The rule must automatically initiate the execution of a playbook.
-Add notes to events that represent data access from a specific IP address to provide the ability to reference the IP address when navigating through an investigation graph while hunting.
-Create a test rule that generates alerts when inbound access to Microsoft Office 365 by the Microsoft Entra test user accounts is detected. Alerts generated by the rule must be grouped into individual incidents, with one incident per test user account.
-