Free SC-401 Exam Braindumps
Administering Information Security in Microsoft 365 (page: 4)

Updated On: 19-Oct-2026
View Related Case Study

You have a Microsoft 365 alert named Alert2 as shown in the following exhibit.

You need to manage the status of Alert2.
To which status can you change Alert2?

  1. The status cannot be changed.
  2. Dismissed only
  3. Investigating only
  4. Active or Investigating only
  5. Investigating, Active, or Dismissed

Answer(s): E

Explanation:

Despite status showing resolved it still can be changed. Select alert > Under Alert status > Actions > select
"Edit comments" > choose new status: Active, Investigating, Dismissed or Resolved. Alert status will change
Note: Alert status
When an alert is created, its status is Active. As you review the details of each alert, you can update its status to any of the states listed below:
Active: default state of the alert until its status is changed
Investigating: alert is under investigation
Resolved: the alert doesn't require further investigation or follow-up
Dismissed: the alert isn't relevant or doesn't need investigation


Reference:

https://learn.microsoft.com/en-us/purview/compliance-manager-alert-policies https://docs.microsoft.com/en-us/microsoft-365/compliance/dlp-configure-view-alerts-policies


View Related Case Study

HOTSPOT (Drag and Drop is not supported)
You have a Microsoft 365 E5 subscription that contains the groups shown in the following table.

The subscription contains the users shown in the following table.

You create the mail flow rules shown in the following table.

For each of the following statements, select Yes if the statement is true. Otherwise, select No.
Note: Each correct selection is worth one point.
Hot Area:

  1. See Explanation section for answer.

Answer(s): A

Explanation:


Box 1: Yes
Yes - If User2 sends an email to User3, the message is encrypted automatically.
User2 is member of Dist1.
Dist1 is a distribution group with the primary email address Dist1@contoso.com.
Rule2 applies if the sender is Dist1@contoso.com.
Rule2 applies Office 365 Message encryption and rights protection.
Box 2: Yes
Yes - If User2 sends an email to User1, the message is encrypted automatically.
With the same logic as for Box 1 above.
Box 3: No
No - If User1 sends an email to Group1, the message is encrypted automatically.
User1 is a member of Group1.
Group1 is a Microsoft group with the primary email address Group1@contoso.com
User3 is the receiver and is not a member of any group.
The rules Rule1 and Rule2 do not apply.


View Related Case Study

HOTSPOT (Drag and Drop is not supported)
You have a Microsoft 365 tenant that uses Microsoft Teams.
You create a data loss prevention (DLP) policy to prevent Microsoft Teams users from sharing sensitive information.
You need to identify which locations must be selected to meet the following requirements:
-▪ Documents that contain sensitive information must not be shared inappropriately in Microsoft Teams.
▪ If a user attempts to share sensitive information during a Microsoft Teams chat session, the message must be deleted immediately.
Which three locations should you select? To answer, select the appropriate locations in the answer area.
Note: Each correct selection is worth one point.
Hot Area:

  1. See Explanation section for answer.

Answer(s): A

Explanation:


Box 1: SharePoint sites
Documents can be stored on SharePoint sties and in OneDrive accounts.
Box 2: OneDrive accounts
Box 3: Teams chat and channel messages
Note: Retention policies can be applied to the following locations:
Exchange email
SharePoint site
OneDrive accounts
Microsoft 365 Groups
Skype for Business
Exchange public folders
Teams channel messages
Teams chats
Teams private channel messages
Yammer community messages
Yammer user messages


Reference:

https://learn.microsoft.com/en-us/microsoft-365/compliance/retention


View Related Case Study

HOTSPOT (Drag and Drop is not supported)
You have a Microsoft 365 E5 tenant that contains a trainable classifier named Classifier1.
You need to increase the accuracy of Classifier1. The solution must use the principle of least privilege.
Which feature should you use and to which role group should you be added? To answer, select the appropriate options in the answer area.
Note: Each correct selection is worth one point.
Hot Area:

  1. See Explanation section for answer.

Answer(s): A

Explanation:


Box 1: Content Explorer
Increase classifier accuracy
Classifiers, like sensitive information types (SIT) and trainable classifiers are used in various kinds of policies to identify sensitive information. Like most such models, sometimes they identify an item as being sensitive that isn't. Or, they may not identify an item as being sensitive when it actually is. These are called false positives and false negatives.
This article shows you how to confirm whether items matched by a classifier are true positive (a Match) or a false positive (Not a match) and provide Match/Not a match feedback. You can use that feedback to tune your classifiers to increase accuracy. You can also send redacted versions of the document as well as the Match,
Not a Match feedback to Microsoft if you want to help increase the accuracy of the classifiers that Microsoft provides.
The Match, Not a match experience is available in:
* -> Content Explorer
Sensitive Information Type Matched Items page
Trainable Classifier Matched Items page
Microsoft Purview Data Loss Prevention (DLP) Alerts page
Box 2: Compliance data administrator
Permissions
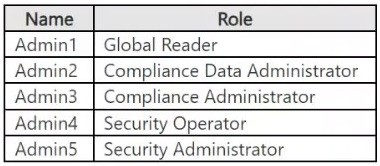
In order to get access to the content explorer tab, an account must be assigned membership in any one of these roles or role groups.
Microsoft 365 role groups
Global administrator
Compliance administrator
Security administrator
*-> Compliance data administrator


Reference:

https://learn.microsoft.com/en-us/microsoft-365/compliance/data-classification-increase-accuracy https://learn.microsoft.com/en-us/microsoft-365/compliance/data-classification-content-explorer


View Related Case Study

HOTSPOT (Drag and Drop is not supported)
You have a Microsoft 365 E5 subscription that contains the resources shown in the following table.

The subscription contains a Windows 11 device named Device1 and has the Microsoft Purview Information
Protection client installed. Device1 contains the resources shown in the following table.

You publish a sensitivity label named Label1 to User1 and Group1.
For each of the following statements, select Yes if the statement is true, Otherwise, select No.
Note: Each correct selection is worth one point.
Hot Area:

  1. See Explanation section for answer.

Answer(s): A

Explanation:


Box 1: Yes
Yes - User1 can apply Label1 to File1.png by using the information protection client.
png is supported file format.
Box 2: No
No - User1 can apply Label1 to Folder2 by using the information protection client.
Folder2 is the root folder.
Note:
Label and protect one or more files
The label and protection that you apply to a file will stay with a file, even if you email the file outside your organization or save it to another location. You can use the following steps to apply a label for the first time or to change the label for already protected files.
1. To open File Explorer, select the file icon on the taskbar or Start menu, or press the Windows logo key New
Windows key logo + E on your keyboard.
2. In File Explorer, right-click the single file, group of files, or folder that you want to protect, and then select
Apply sensitivity label with Microsoft Purview.
Notice: When you select a folder, all the files in that folder and any subfolders are automatically selected for the labeling and protection options that you set. However, new files that are created in that folder or its subfolders in the future will not be automatically configured with those options.
3. Etc.
Box 3: Yes
Yes- User1 can apply Label1 to File1.docx by using the information protection client.
Docx is supported file format.
Note: The following folders are excluded from classifying and labeling by the information protection client:
Windows
Program Files (\Program Files and \Program Files (x86))
\ProgramData
\AppData (for all users)


Reference:

https://learn.microsoft.com/en-us/purview/information-protection-client


Viewing page 4 of 60
Viewing questions 16 - 20 out of 291 questions


Post your Comments and Discuss Microsoft SC-401 exam prep with other Community members:

AI Tutor AI Tutor 👋 I’m here to help!