Free AZ-802 Exam Braindumps
Administering Windows Server Questions 9–13 (page: 5)

Updated On: 29-Oct-2026
View Related Case Study

HOTSPOT (Drag and Drop is not supported)
Your network contains the domains shown in the following exhibit.

You need to establish trust relationships as shown in the following exhibit.

Which type of trust can you use for Trust1 and Trust2? To answer, select the appropriate options in the answer area.
Note: Each correct selection is worth one point.
Hot Area:

  1. See Explanation section for answer.

Answer(s): A

Explanation:


Trust1: Shortcut trust only
Trust2: Forest trust or external trust only
Trust1 connects two domains within the same forest, so a shortcut trust can be used to optimize authentication between them. Trust2 connects domains in separate forests; a forest trust can establish transitive trust between the forests, while an external trust can establish a nontransitive trust between the specified domains.


View Related Case Study

Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com.
You need to identify which server is the PDC emulator for the domain.
Solution: From Active Directory Sites and Services, you right-click Default-First-Site-Name in the console tree, and then select Properties.
Does this meet the goal?

  1. Yes
  2. No

Answer(s): B

Explanation:

The properties of Default-First-Site-Name do not identify the domain’s PDC emulator. The PDC emulator is a domain-level FSMO role and can be identified through tools such as Active Directory Users and Computers, Active Directory Domains and Trusts, or PowerShell commands such as Get-ADDomain.


View Related Case Study

HOTSPOT (Drag and Drop is not supported)
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com.
The domain contains a user named User1 and two global security groups named Group1 and Group2. User1 is a member of both groups.
A Group Policy Object (GPO) named GPO1 is linked to the domain. GPO1 contains the following User Configuration preference items.

For each of the following statements, select Yes if the statement is true. Otherwise, select No.
Note: Each correct selection is worth one point.
Hot Area:

  1. See Explanation section for answer.

Answer(s): A

Explanation:


Box 1: No
No, drive S will not be mapped.
Failed Targeting: Item-level targeting requires both membership in the first global group and an IP address in the range of 10.10.0.0 to 10.10.255.255.
IP Mismatch: The sign-in IP address (10.20.5.20) is outside the specified range. Because the targeting rule uses an AND condition, the entire filter evaluates to false.
Removal Rule: The option Remove this item when it is no longer valid is selected, meaning the preference item will not apply or will be removed if the conditions are not met.
Box 2: Yes
Yes, the user will not have driven S in File Explorer after signing in.
Targeting Condition Fails: Item-level targeting requires both the first global group and the IP address range 10.10.0.0 through 10.10.255.255. Removing the user from Group1 makes this targeting rule false.
Removal Option Active: The setting "Remove this item when it is no longer valid" is selected.
When targeting fails, the Group Policy engine actively removes the configuration.
Continuous Evaluation: "Apply once and do not reapply" is disabled. This means the preference re-evaluates the targeting rules at every sign-in and policy update, enforcing the removal when conditions are no longer met.
Box 3: Yes
Yes, the shortcut is created once and never reapplied or recreated on future Group Policy refreshes.
Targeting is met: The targeting uses an OR condition (member of the second global group OR local file exists). Because the user is in the second global group, the targeting condition evaluates to true even though the local file C:\Program files\SalesApp\SalesApp.exe does not exist on the client computer.
Apply once setting: The option Apply once and do not reapply is selected for the shortcut. Group Policy Preferences applies the setting a single time and ignores it on all subsequent policy refreshes.


Reference:

https://learn.microsoft.com/en-us/windows-server/identity/ad-ds/manage/understand-security-groups


View Related Case Study

Your network contains an Active Directory Domain Services (AD DS) forest named contoso.com. The forest contains the domain controllers shown in the following table.
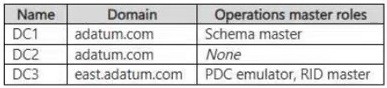
You have a partner organization that has an AD DS forest named fabrikam.com.
You create a trust relationship between contoso.com and fabrikam.com.
You need to configure selective authentication for the trust relationship.
Which domain controller should be granted permissions to fabrikam.com?

  1. DC1
  2. DC2
  3. DC3
  4. DC4

Answer(s): D

Explanation:

For selective authentication across a forest trust, the PDC emulator in the trusted forest must be permitted to authenticate to the domain controllers in the trusting forest so that trust-related authentication can function correctly. DC4 holds the PDC emulator role.


Reference:

https://learn.microsoft.com/en-us/troubleshoot/windows-server/windows-security/windows-updates-add-new-ntlm-pass-through-authentication-protections


View Related Case Study

Your network contains an Active Directory Domain Services (AD DS) domain. The network also contains 20 domain controllers, 100 member servers, and 10,000 client computers.
You have a Group Policy Object (GPO) named GPO1 that contains Group Policy preferences.
You plan to link GPO1 to the domain.
You need to ensure that the preferences in GPO1 apply only to domain member servers and NOT to domain controllers or client computers. All the other Group Policy settings in GPO1 must apply to all the computers. The solution must minimize administrative effort.
Which type of item-level targeting should you use?

  1. Security Group
  2. Environment Variable
  3. Domain
  4. Operating System

Answer(s): D

Explanation:

Operating System item-level targeting lets you select Server as the computer role, limiting the preference items to member servers. Item-level targeting affects only the configured preference items, so the other settings in GPO1 continue to apply to all computers in the domain.


Viewing page 5 of 37
Viewing questions 21 - 25 out of 224 questions


Post your Comments and Discuss Microsoft AZ-802 exam prep with other Community members:

AI Tutor AI Tutor 👋 I’m here to help!