Case Study
This is a case study. Case studies are not timed separately. You can use as much exam time as you would like to complete each case. However, there may be additional case studies and sections on this exam. You must manage your time to ensure that you are able to complete all questions included on this exam in the time provided.
To answer the questions included in a case study, you will need to reference information that is provided in the case study. Case studies might contain exhibits and other resources that provide more information about the scenario that is described in the case study. Each question is independent of the other questions in this case study.
At the end of this case study, a review screen will appear. This screen allows you to review your answers and to make changes before you move to the next section of the exam. After you begin a new section, you cannot return to this section.
To start the case study
To display the first question in this case study, click the Next button. Use the buttons in the left pane to explore the content of the case study before you answer the questions. Clicking these buttons displays information such as business requirements, existing environment, and problem statements.
When you are ready to answer a question, click the Question button to return to the question.
Overview
Proseware, Inc. is a financial services company that has a main office in New York City and a branch office in San Francisco.
Existing Environment. Hybrid Environment
Proseware has an on-premises Active Directory Domain Services (AD DS) forest named corp.proseware.com that syncs with a Microsoft Entra tenant named proseware.com.
Proseware has an Azure subscription that is linked to proseware.com.
Proseware has an internal certification authority (CA).
Existing Environment. Network Infrastructure
The offices contain the resources shown in the following table.
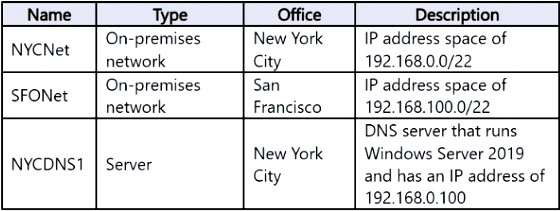
NYCNet connects to Azure by using an ExpressRoute circuit.
SFONet connects to Azure by using a Site-to-Site (S2S) VPN.
Existing Environment. Azure Resources
The Azure subscription contains the virtual networks and subnets shown in the following table.
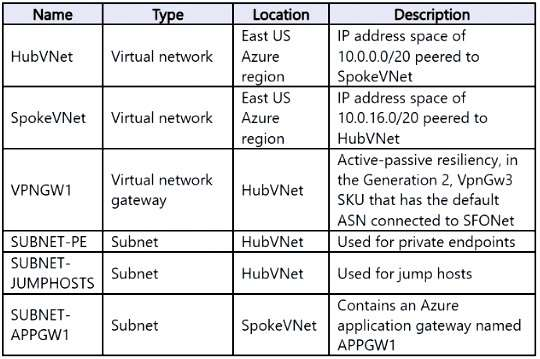
The subscription contains four virtual machines named VM1, VM2, VM3, and VM4. VM1 and VM2 host an app named App1.
VM3 and VM4 host a web app named App2 that is accessed by using a FQDN of app2.proseware.com. Users access app2.proseware.com by using HTTP or HTTPS.
VM1, VM2, and VM4 are connected to SpokeVNet.
The subscription contains Application Gateway resources shown in the following table.
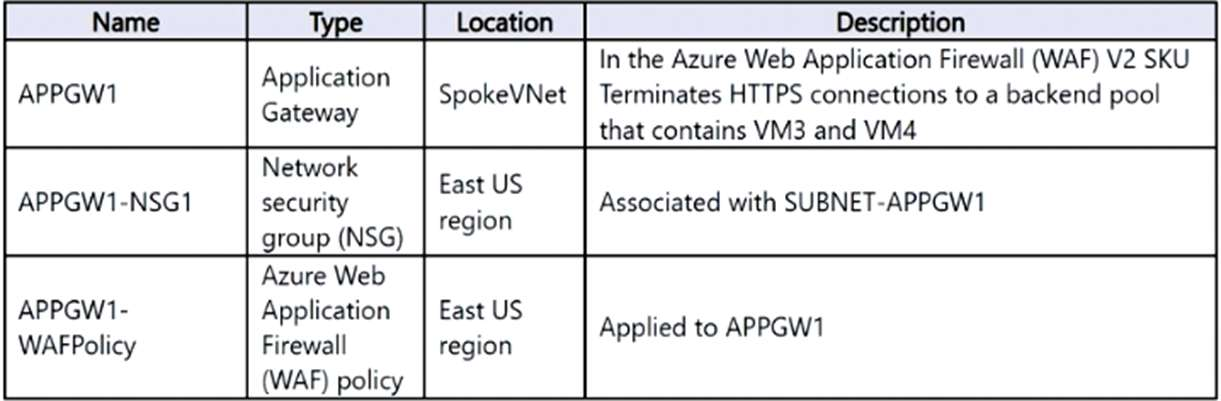
The subscription contains an Azure Front Door Standard profile named FD1. FD1 contains a single origin group that targets APPGW1 by using the default endpoint name.
HubVNet connects to NYCNet by using an ExpressRoute gateway named ERGW1.
Planned Changes and Requirements. Planned Changes
Proseware plans to implement the following changes:
Deploy an Azure Private DNS Resolver named PRDNS1 to HubVNet and link PRDNS1 to SpokeVNet.
Create a DNS forwarding ruleset named DNSRS1 and associate DNSRS1 with PRDNS1.
Deploy Azure Virtual Network Manager and implement the following rules:
- Allow inbound connections on TCP port 3389 from the on-premises networks to SUBNET-JUMPHOSTS.
- Block inbound connections on TCP port 80 from the internet to SpokeVNet. Ensure that Azure Virtual Network Manager rules take precedence over conflicting NSG rules.
Deploy two network virtual appliances (NVAs) named NVA1 and NVA2 to HubVNet.
Deploy a gateway load balancer named LBGW1 to HubVNet.
Configure LBGW1 to inspect traffic on TCP ports 443, 1433, and 1434 from LBS1 by using NVA1 and
NVA2.
Ensure that all the traffic to App2 is processed by using FD1.
Planned Changes and Requirements. Connectivity requirements
Proseware identifies the following connectivity requirements:
Minimize the complexity of the Azure Virtual Network Manager deployment.
Route traffic between NYCNet and SFONet via the ExpressRoute circuit and the S2S VPN.
Ensure that remote users on Windows 11 devices can connect to HubVNet by using a Point-to-Site (P2S)
VPN and their proseware.com credentials.
Planned Changes and Requirements. Security requirements
Proseware identifies the following security requirements:
Whenever possible, use the internal CA.
Ensure that all connections routed via APPGW1 use end-to-end encryption.
Ensure that user connections to Azure-hosted apps use end-to-end encryption.
Ensure that all inbound internet traffic to app2.proseware.com is routed via FD1.
Prevent devices that connect to NYCNet from accessing Azure services that use private endpoints.
Enable the virtual machines that connect to HubVNet and SpokeVNet to access Azure services that use private endpoints.
Planned Changes and Requirements. General requirements
Proseware identifies the following general requirements:
Minimize the IP address space required to deploy platform-managed resources to the virtual networks.
From SpokeVNet, resolve name resolution requests for the azure.proseware.com namespace and the corp.proseware.com namespace by using PRDNS1.
Whenever possible, minimize administrative effort.